Security tip 11 · Test yourself
Test your domain in five minutes.
Two free test sites check website, email and connection against modern standards and tell you what is missing. We tested wi24rd.com – and it did not get 100%.
Last checked 1 November 2026
Short answer
Run your domain through internet.nl (website, email and connection) and the Danish sikkerpånettet.dk. Both give a percentage and a list of what is missing – typically DNSSEC, DMARC or modern TLS. Fix the top item first and test again.
- Time
- ~5 min per test
- Price
- Free no account
- Tests
- Web · mail · net
- Needs
- Just the domain name
Why
You cannot see it with your eyes.
A website can look fine and still use weak encryption, lack protection against fake emails or not be signed in DNS. These are things an attacker can use, and nobody notices until someone tests.
The Dutch internet.nl is run by a public-private platform in the Netherlands, and the code is open. Punktum dk, which runs .dk, uses the same code in the Danish version sikkerpånettet.dk and supports the Dutch project. The tests are the same; the Danish one explains in Danish.
What is tested
- Website
- IPv6, DNSSEC, HTTPS and encryption, security headers, security.txt and RPKI.
- SPF, DKIM and DMARC (tip 6), encrypted transport (STARTTLS and DANE) and DNSSEC.
- Connection
- Whether your own internet connection supports IPv6 and checks DNSSEC signatures.
Step by step
Five steps, about 5 minutes.
Test the website
Enter the domain under Test your website and press start. After half a minute you get a score and a list of green, orange and red.
Test the email
Enter the domain – or an address on it – under Test your email. The test looks at what other mail servers see when they send to you.
Read the red first
Open each red item. The technical details say exactly what is missing, and each section links to how to fix it.
Fix what you can
Many red items are fixed in a few clicks when the domain is in Cloudflare: DNSSEC and HTTPS in tip 3, SPF, DKIM and DMARC in tip 6. If you cannot do it yourself, send the link to the result to whoever looks after your website or email.
Test again
Every test has a permanent link. Run it again after a change, and keep the link – then you can see the progress next year.
wi24rd.com in the test
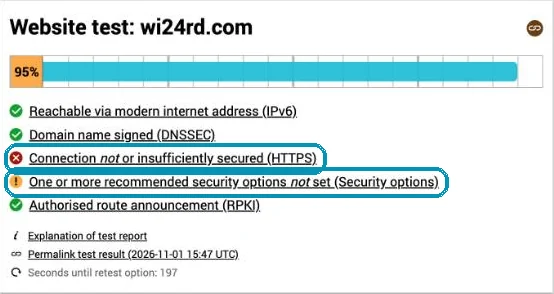
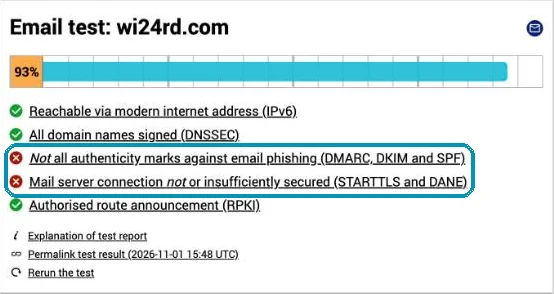
95% and 93%. Here is why.
We tested wi24rd.com on 1 November 2026. IPv6, DNSSEC, certificate, HSTS and RPKI passed. The red is about two things:
- Older encryption methods. Cloudflare still offers some older methods for old browsers. They are not broken, but the test calls them insufficient. On the free plan they cannot be switched off; that needs the add-on Advanced Certificate Manager. New browsers use the modern methods.
- DMARC is in monitoring. wi24rd.com’s DMARC policy is
p=nonewhile we collect reports. When they show that only genuine emails get through, it is tightened toquarantine– exactly as in tip 6.
The point: red is not always a disaster. It is a list you need to understand – and some items are a deliberate choice.
Honest about the limits
- It tests standards, it is not a security audit. It does not find holes in your software, weak passwords or open ports – for the last one there is tip 1.
- The test is strict on purpose. 100% is the goal, but not everything can be fixed on every platform.
About this tip
wi24rd.com was tested on internet.nl on 1 November 2026. The information about sikkerpånettet.dk comes from internet.nl’s own news item on the cooperation with Punktum dk. The Advanced Certificate Manager requirement is in Cloudflare’s documentation.
The man behind Wi24rd has used Cloudflare himself since he saw them at Black Hat in London in 2015. Wi24rd has no financial interest in Cloudflare – no money, discounts or services.
Missing a tip?
Write what you would like explained. The next security tip could be yours.